Posts

Showing posts with the label Hacking latest news

What Is the Most Secure VPN Protocol?
Image
VPN products vary greatly in convenience, efficiency, and security. If security is a serious concern, an organization needs to pay close attention to the protocols a service supports. Some widely used protocols have significant weaknesses, while others offer state-of-the-art security. The best of the lot today include OpenVPN and IKEv2. Understanding VPN protocols What’s called a VPN protocol is actually a collection of protocols. There are several functions which every VPN has to manage: – Tunnelling  A VPN’s basic function is to deliver packets from one point to another without exposing them to anyone on the path in between. To do this, it encapsulates all data in a format which the client and server understand. The side sending the data puts it into the tunneling format, and the receiving side extracts it. – Encryption  By itself, tunneling provides no protection. Anyone can extract the data. It also has to be encrypted over the transmission path. The receiving si...

Swiss Government Invites Hackers to Pen Test Their Voting System

Image
The Swiss government is eager to ensure that its e-voting system is safe and secure for those casting their votes. To ensure that’s the case, they issued a press release looking for “Interested hackers from all over the world to attack the system.” This will be in the form of a public intrusion test or PIT session. Public Intrusion Test The public intrusion test (PIT) will run from February 25 until March 2 and offer cash rewards depending on what the hackers are able to do. There are a set of rules  attached to this PIT, which set out the basics of the test, and the qualifying vulnerabilities. The rewards for this test range from $100 to $30,000 based on CHF points (1 CHF point is roughly equivalent to 1 USD.) There is set to be a mock e-voting session planned for the last day of testing on 24 March. However, hackers can attack the e-voting system before this date as well. Registration Anyone wanting to participate in the test  has t...

How Just Opening A Site In Safari Could Have Hacked Your Apple macOS

Image
Earlier this week Dropbox team unveiled details of three critical vulnerabilities in  Apple macOS operating system, which altogether could allow a remote attacker to execute malicious code on a targeted Mac computer just by convincing a victim into visiting a malicious web page. The reported vulnerabilities were originally discovered by  Syndis , a cybersecurity firm hired by Dropbox to conduct simulated penetration testing attacks as Red Team on the company's IT infrastructure, including Apple software used by  Dropbox. The vulnerabilities were discovered and disclosed to Apple security team in February this year, which were then patched by Apple just over one month later with the release of its March security updates. DropBox applauded Apple for its quick response to its bug report. Source: Google Images According to DropBox, the vulnerabilities discovered by Syndis didn't just affect its macOS fleet, but also affected all Safari users running the latest ...

HSBC Bank Suffers Data Breach

HSBC became a target in October. The bank confirms it suffered a data breach whereby account details of some of their online customers was exposed. HSBC believes the perpetrators carried out the attacks in October 4, 2018 and October 14, 2018. Fortunately only a small amount of customers were affected, reportedly less than 1%. For those affected, they had the following information stolen: full name, mailing address, date of birth, phone number, email address, account numbers, account types, account balances, transaction history, payee account information, and statement history where available. As a safety measure, affected accounts were suspended online to guard against further unauthorized entry. Impacted user received calls/emails where they were prompted to change their banking details before accessing their accounts. American Banker was able to talk with Rob Sherman, U.S. head of media relations for the bank, who said, “HSBC regrets this incident, and we take our responsibi...

Flaw in System could Crash Linux Systems

Image
Researchers have discovered a critical flaw in Systemd which can be exploited by attackers to crash a Linux system. The vulnerability (CVE-2018-15688) was discovered by security researcher Felix Wilhelm of the Google security team and said that the flaw resides in the DHCPv6 client of the open-source Systemd management suite. “systemd-networkd contains a DHCPv6 client which is written from scratch and can be spawned automatically on managed interfaces when IPv6 router advertisement are received” said in the post published by Researchers. The attackers can exploit the vulnerability using a malicious crafted DHCPv6 packet and change parts memory in vulnerable systems, making it vulnerable to remote code execution. Source:Google Image The DHCPv6 client is automatically activated if the IPv6 support is enabled and start packets arrive for processing. A rogue DHCPv6 server on a network, or in an ISP can wake up DHCPv6 clients by sending specially craft...

Ransom Warrior Victims can now retrieve files for free

Image
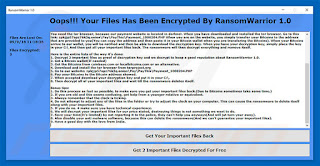
Researchers at Check Point have figured out the encryption method used by RansomWarrior. The Ransomware was developed in India. The ransomware has targeted Windows users, the payload is delivered as an executable under file name “A Big Present.exe”  if the application is executed it will encrypt files with a .THBEC  extension. The victims are given a link to the dark web website that takes payments in Bitcoin. The Ransomware offers the victims to decrypt two files for free, however if the victims don’t pay the ransom they will not get the rest of their files back. The ransomware cheekily has a sentence saying that the police can’t help you. How Did The Researchers Break the Encryption? source img:https://www.pcrisk.com Researchers at Check Point found the malware was developed by some inexperienced hackers, the company was able to retrieve decryption keys from the malware. Check Point succeeded due to the weak encryption used by the ransomware. The Ransomw...

Hackers Target Smartphones to Mine Cryptocurrencies

Image
This new type of cybe rattack is called "cryptojacking" by security experts. It "consists of entrapping an internet server, a personal computer or a smartphone to install malware to mine cryptocurrencies," said Gerome Billois, an expert at the IT service management company Wavestone. Mining is basically the process of helping verify and process transactions in a given virtual currency. In exchange miners are now and then rewarded with some of the currency themselves. Legitimate mining operations link thousands of processors together to increase the computing power available to earn cryptocurrencies. Mining bitcoin, ethereum, monero and other cryptocurrencies may be very profitable, but it does require considerable investments and generates huge electricity bills. But hackers have found a cheaper option: surreptitiously exploiting the processors in smartphones. To lure victims, hackers turn to the digital world's equivalent of the Trojan horse subterfuge of Gr...

New Open Source Tool Developed to Detect Twitter Botnets

Security experts from Duo Security have developed some open source tools with accompanied documentation that discusses the techniques used to identify large botnets. The experts have developed these tools after analysing 88 million Twitter accounts and more than half-a-billion tweets. The company has constructed the dataset using Twitter’s API. Duo Security has also collected the user’s profile name, follower count, avatar, bio, the contents of the tweets and social network connections. The most conventional way of utilizing data science techniques require the developers to create a classifier that will classify Twitter accounts that are automated by the bots. Researchers have identified the accounts based on factors such as the number of digits, Entropy, followers/following ratio, number of tweets and likes for that tweets. The tools developed by the researchers can be used to investigate fraudulent activities that occur on the Twitter. The tools can also be used to monitor the evo...

Reddit Hacked – Emails, Passwords, Private Messages Stolen

                This time the victim is Reddit... seems someone is really pissed off with Reddit's account ban policy or bias moderators. Reddit social media network today announced that it suffered a security breach in June that exposed some of its users' data, including their current email addresses and an old 2007 database backup containing usernames and hashed passwords. According to Reddit, the unknown hacker(s) managed to gain read-only access to some of its systems that contained its users' backup data, source code, internal logs, and other files. In a post published to the platform Wednesday, Reddit Chief Technology Officer Christopher Slowe admitted that the hack was a serious one, but assured its users that the hackers did not gain access to Reddit systems. "[The attackers] were not able to alter Reddit information, and we have taken steps since the event to further lock down and rotate all production secrets and API keys, and to...